In the traditional office, a “Clean Desk” policy was a simple habit: shred the sensitive stuff, lock it away, and don’t leave passwords where […]
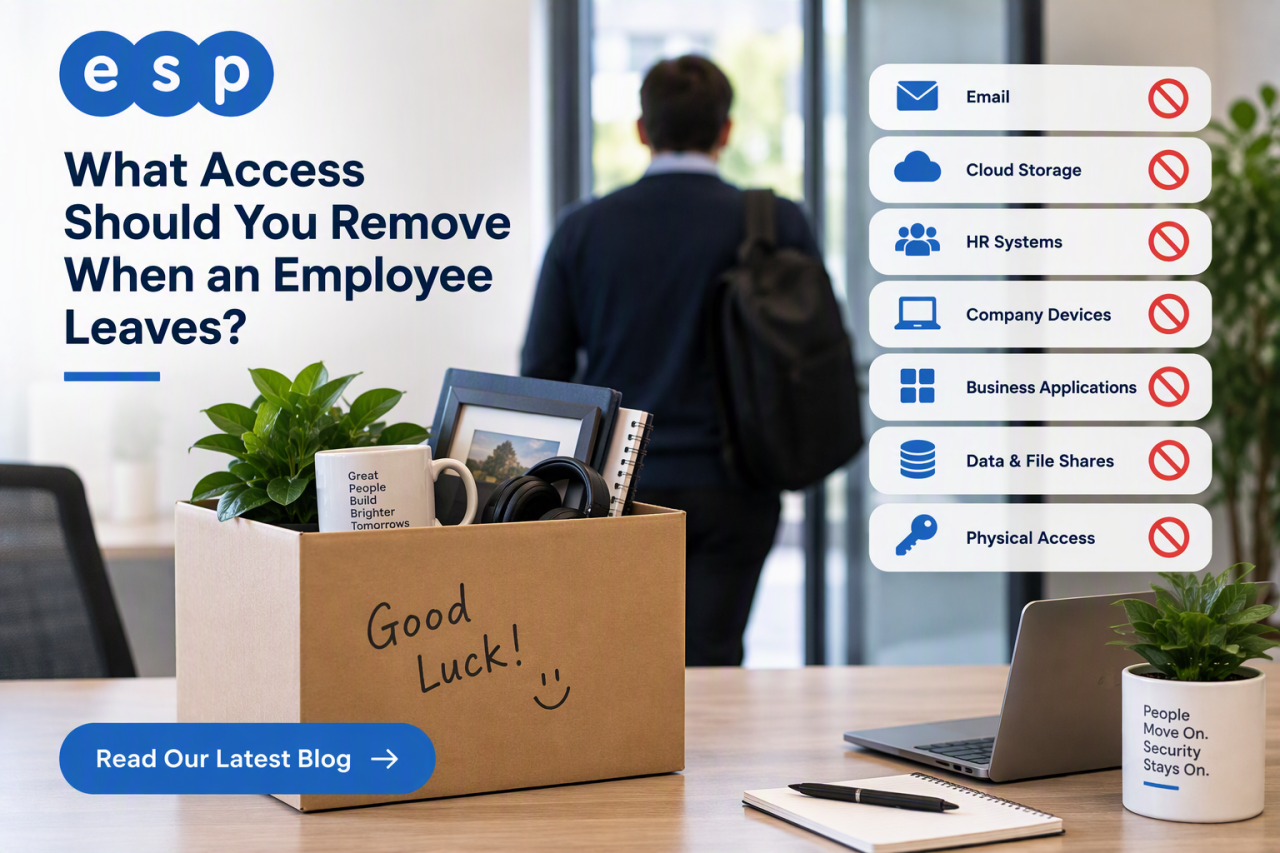
When an employee leaves, remove their ability to sign in to company systems at the agreed leaving time, then work through every other route they used […]
Most small businesses aren’t breached because they have no security at all. They’re breached because a single stolen password becomes a master key to […]
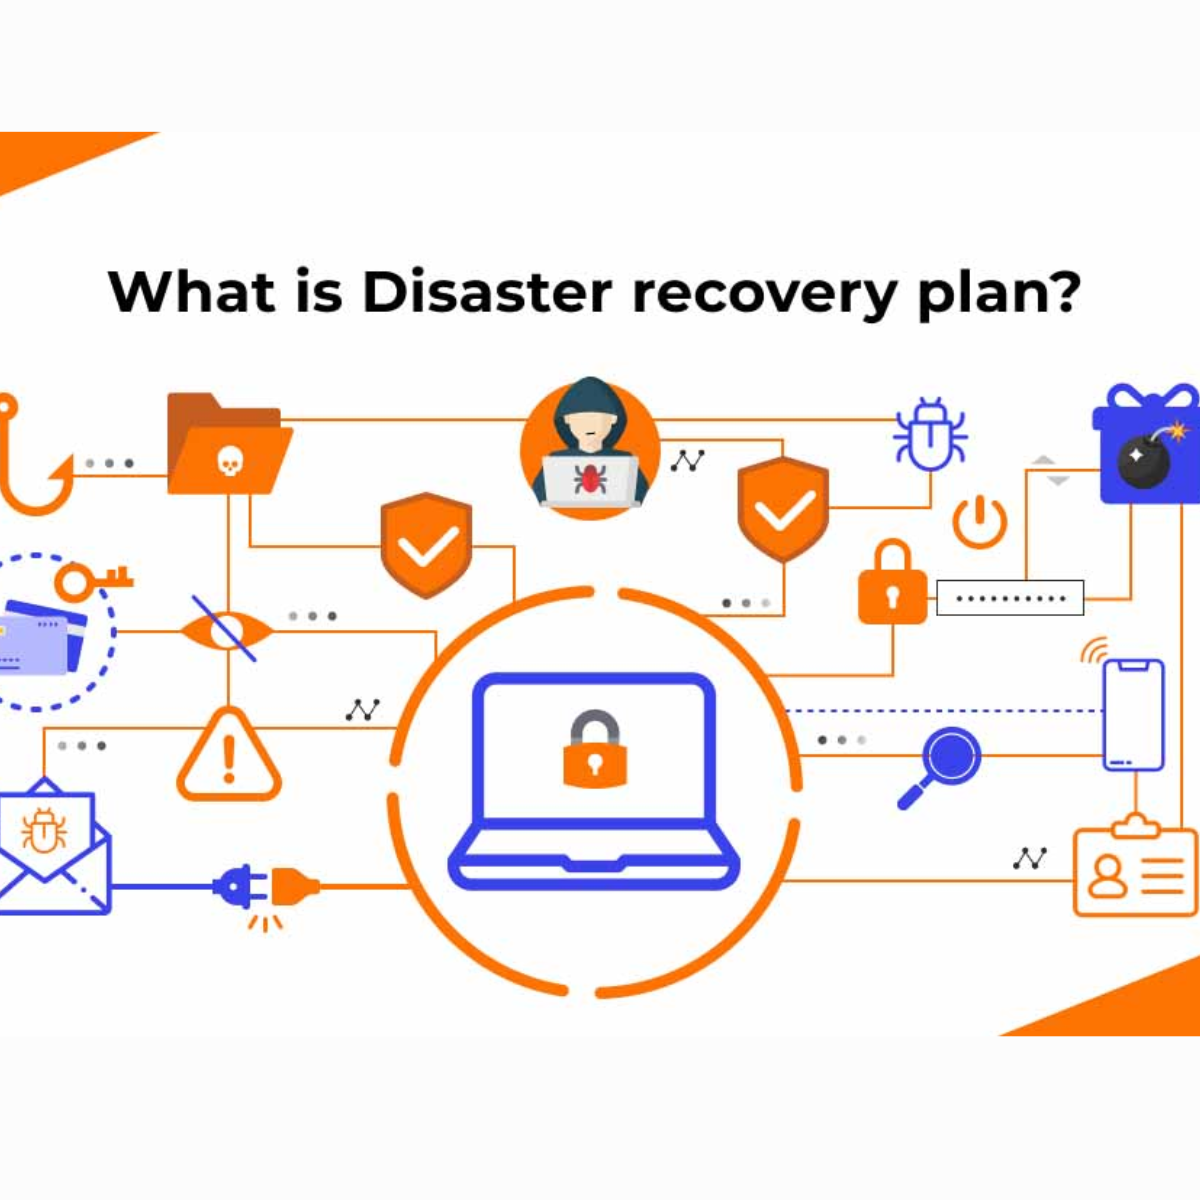
An IT disaster recovery plan, often shortened to DRP, is a documented set of steps your business follows to restore IT systems, data and infrastructure after […]

It usually starts small. Someone uses an AI tool to refine a difficult email. Someone enables an AI add-on inside a SaaS app because […]

Ransomware isn’t a jump scare. It’s a slow build.
In many cases, it begins days, or even weeks, before encryption, with […]
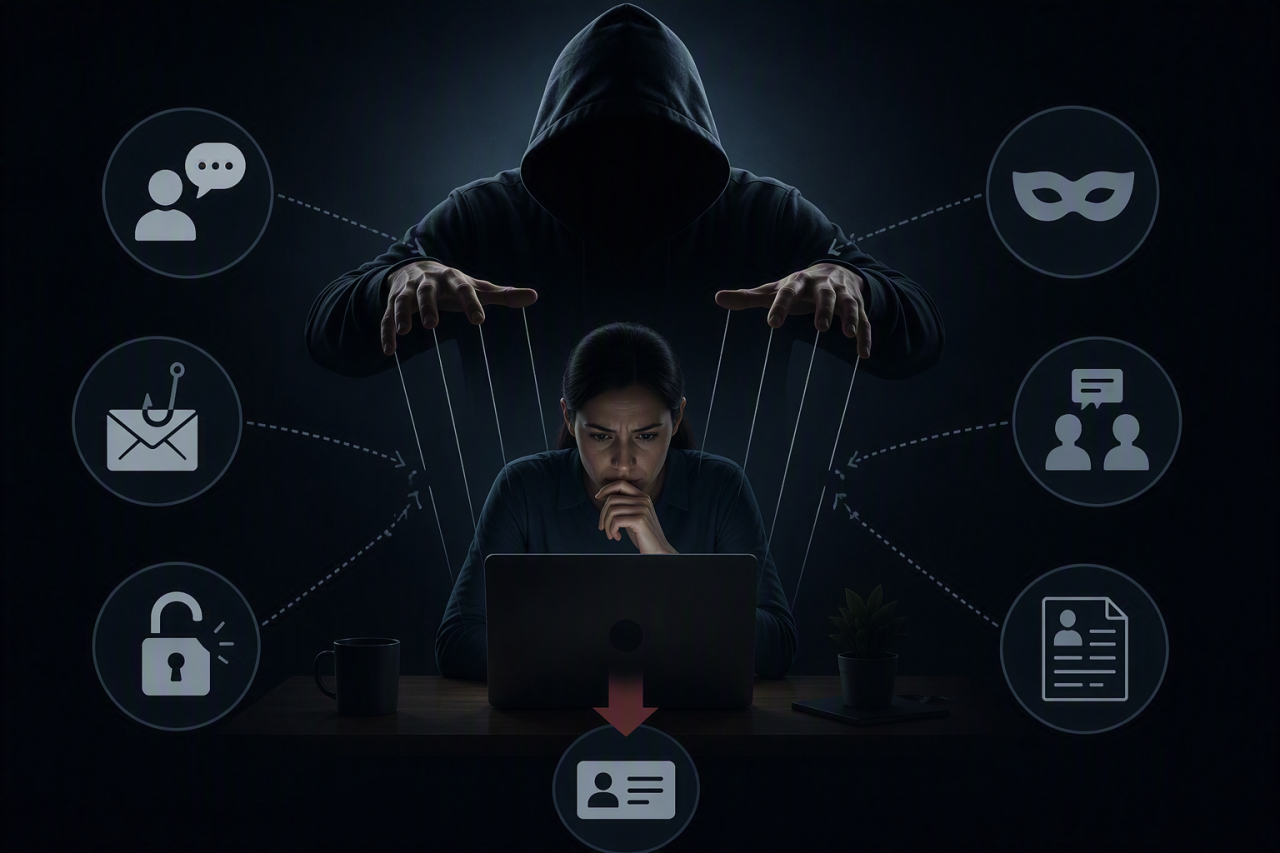
When most people think about cybercrime, they picture hackers breaking through firewalls, writing malicious code or exploiting software vulnerabilities.
In reality, many successful cyber-attacks don’t begin […]
Cyber-attacks often bring to mind sophisticated malware, nation-state actors and highly technical exploits. However, one of the most significant UK cyber incidents of recent months appears to have started […]