IT lifecycle management is the structured process of planning, purchasing, deploying, maintaining, replacing and securely disposing of your organisation’s technology assets.
It covers physical equipment such as […]
Most businesses should replace laptops and desktops every four years, and in fact servers should come under the same advice. There are many reasons for this […]

Ransomware isn’t a jump scare. It’s a slow build.
In many cases, it begins days, or even weeks, before encryption, with […]
When most people think about cybercrime, they picture hackers breaking through firewalls, writing malicious code or exploiting software vulnerabilities.
In reality, many successful cyber-attacks don’t begin […]
Cyber-attacks often bring to mind sophisticated malware, nation-state actors and highly technical exploits. However, one of the most significant UK cyber incidents of recent months appears to have started […]
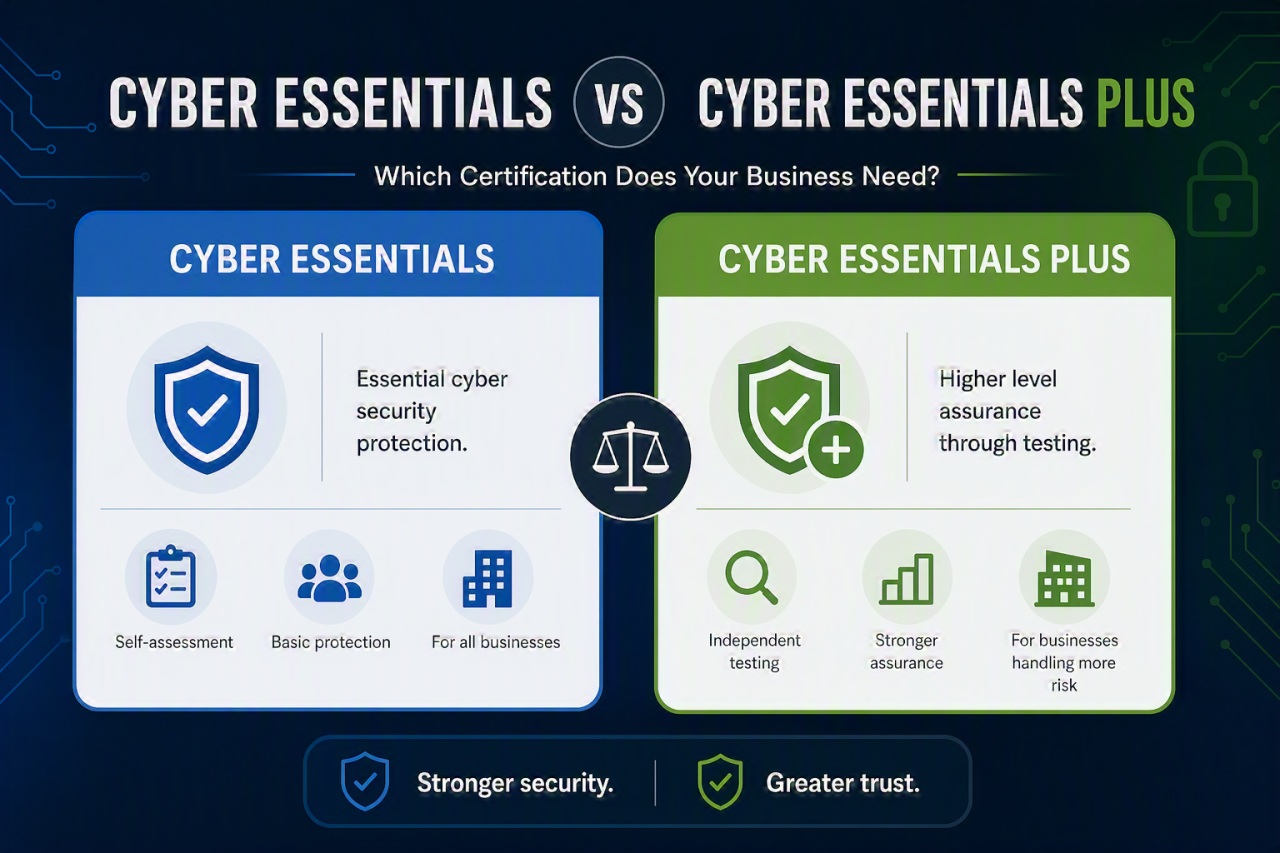
The verdict: most UK businesses should start with basic Cyber Essentials, then move to Cyber Essentials Plus within three months if they handle sensitive data or […]

If you want to uncover unsanctioned cloud apps, don’t begin with a policy. Start with your browser history.
The cloud environment […]
Small businesses are the most common ransomware target by volume of incidents, even though many small business owners assume hackers focus on larger organizations. […]