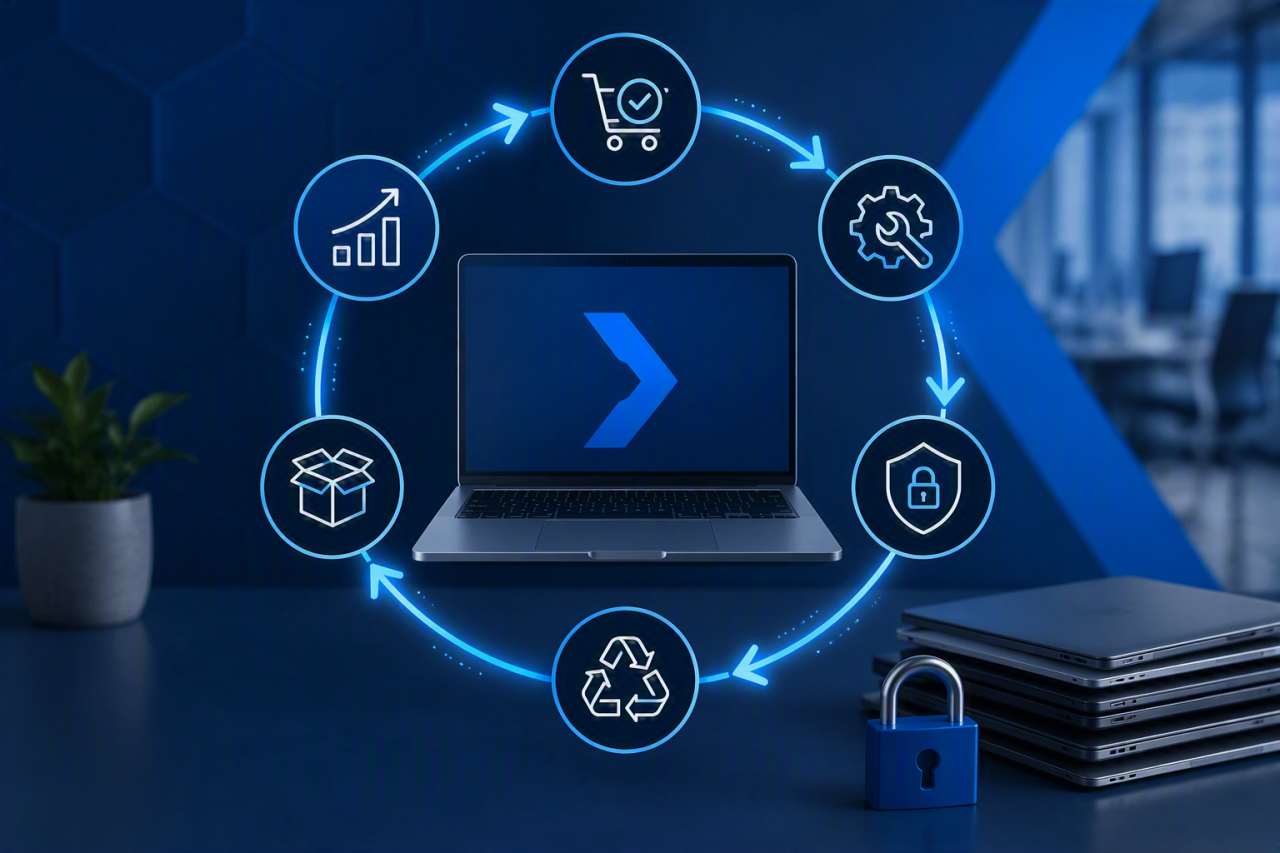
IT lifecycle management is the structured process of planning, purchasing, deploying, maintaining, replacing and securely disposing of your organisation’s technology assets.
It covers physical equipment such as […]
Most businesses should replace laptops and desktops every four years, and in fact servers should come under the same advice. There are many reasons for this […]
Most small businesses aren’t falling short because they don’t care. They’re falling short because they didn’t build their security strategy […]
Most small businesses aren’t breached because they have no security at all. They’re breached because a single stolen password becomes a master key to […]
An IT disaster recovery plan, often shortened to DRP, is a documented set of steps your business follows to restore IT systems, data and infrastructure after […]

It usually starts small. Someone uses an AI tool to refine a difficult email. Someone enables an AI add-on inside a SaaS app because […]

Ransomware isn’t a jump scare. It’s a slow build.
In many cases, it begins days, or even weeks, before encryption, with […]
When most people think about cybercrime, they picture hackers breaking through firewalls, writing malicious code or exploiting software vulnerabilities.
In reality, many successful cyber-attacks don’t begin […]